Cloudflare Launchpad About the Launchpad

About ManticoreAI

From the operator's desk to ShieldProbe.

ManticoreAI makes ShieldProbe, penetration testing that proves what an attacker can exploit in your web applications, APIs, networks and servers. Our founder, Saeid Atabaki, has spent fifteen years in offensive security. In 2020 he started building that method into software.

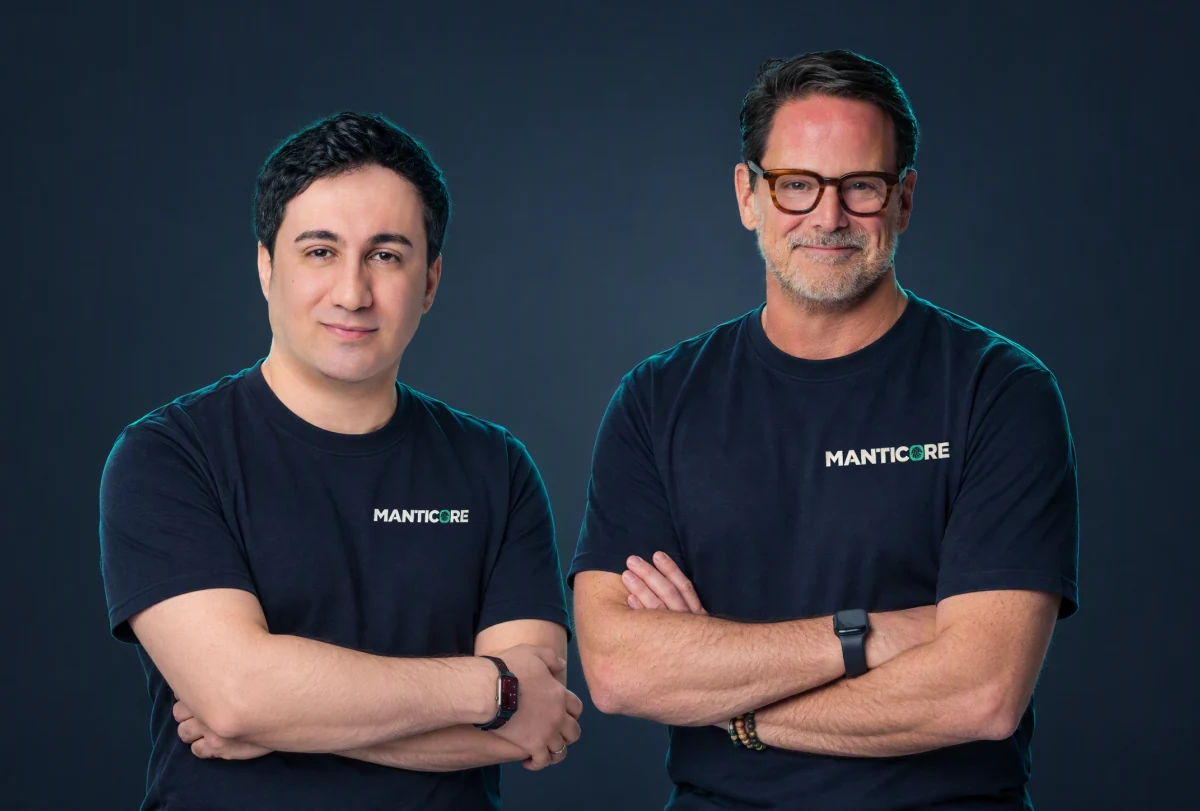
Saeid Atabaki (left) and John Loveland (right) wearing ManticoreAI T-shirts

Offensive research meets security-services experience.

Research since 2020. ManticoreAI Inc., Wilmington, Delaware, with a Singapore subsidiary.Trust Center Responsible disclosureSee an illustrative sample report

In production with telecommunications, financial services and technology companies in the US and Singapore. A Cloudflare Workers Launchpad, Cohort 5 participant.

How we work

What you can hold us to.

ManticoreAI is on the CREST accreditation Pathway, which is distinct from membership. Our founders' personal credentials are listed under Leadership.

  • Proof, not claims.

    Every Assess finding carries the evidence to reproduce it: the captured request and response or tool output, the payload and the replay steps. If we cannot reproduce it, it is not a finding.

  • Auditor, not Author.

    In an Assess engagement, AI authors findings. A named consultant reviews and approves each one before it is visible to you, enters a report or drives a Defend rule. The gate is enforced in the database.

  • Inference through Azure.

    Inference uses Microsoft-hosted OpenAI models through Azure Foundry. Microsoft processes prompts and outputs; they are not made available to OpenAI.

  • Scope honesty.

    Web applications, APIs, networks and servers, internal or external, within an agreed scope. We decline the rest rather than stretch the story.

Leadership

The people
behind the work.

One built the platform and holds the credentials behind its method. The other spent twenty-five years on the buying side of security services. Behind them, engineers, penetration testers and sellers across the United States and Singapore.

Founder and CEO. Principal engineer.

Saeid Atabaki

Fifteen years of offensive work against banks, telecommunications companies and critical infrastructure. He started building the platform in 2020, before large language models were a product, because scanners never found what his teams found and consultants could not scale the way software ships.

Background
Former Director, Trustwave SpiderLabs APAC. Built OCBC Bank's internal red team.
Credentials
OSEE. Previously held CREST CCSAS (2019 to 2022).
Community
Former member of the CREST Red Team Focus Group.
LinkedIn

Co-founder and Chief Growth Officer.

John Loveland

Twenty-five years running and selling security services to enterprises. He has sat on both sides of the pentest RFP, which is why the buying motion here looks like a consultancy's and the delivery does not.

Background
Global Head of Cyber Strategy at Verizon, where he co-led a $500M+ security practice. Senior Managing Director, PwC cybersecurity advisory.
Founded
S3 Partners, acquired.
LinkedIn

Since 2020

Five years of research before the first customer.

The order matters. The driver came before the agents, the agents before the product, and the product before the first customer.

  1. 2020

    Kernel-level context driver

    Research begins on a driver that watches process I/O at the native level, so an AI can drive real tools the way an operator does instead of calling wrappers around them.

  2. 2021–22

    A pentest operating system, not a chatbot

    A persistent agent that tracks targets, credentials, footholds and hypotheses across an engagement and keeps an attack plan.

  3. 2023

    Encoded methodology

    Fifteen years of red-team method, attack-tree heuristics and bank playbooks compiled into the reasoning the agents work from.

  4. 2024

    Defend and Fix

    Generative Counter Exploits derived from supported findings, and code fixes drafted from the attack. Developers review the change and raise the pull request.

  5. 2025

    Continuous, in developer preview

    Selected retests run on the repository events you enable, through your GitHub or Azure DevOps workflows.

  6. 2026

    In production

    ShieldProbe in production with enterprises in telecommunications, financial services and technology across the US and Singapore.

Your next step

Scope a pilot on one application.

We agree targets, authorization and access with you. You judge the evidence before you expand.

Discuss an engagement